



ZDNET’s key takeaways
- openSUSE Leap is getting an immutable mode.
- openSUSE already includes plenty of security features.
- This addition should make Leap one of the most secure distros.
I’ve been a fan of SUSE and openSUSE for a long time. I actually remember SUSE Linux before it was SUSE Enterprise Linux or SUSE Enterprise Linux Desktop. Even back then, the distribution was a power user’s dream come true.
One reason for this was its security.
openSUSE has been, for a very long time, one of the more secure of the “mainstream” Linux distributions. And in German-speaking countries, openSUSE is quite popular due to its ties to the German company SUSE.
Also:This Linux distro makes openSUSE accessible to all – even newbies should take a look
Starting with version 16.1, openSUSE Leap (the stable version of the distro) is adding another layer to its security that should further elevate it as one of the more secure distributions on the market. That layer is immutable mode.
According to the official openSUSE blog, “Leap 16.1 is the first Leap release to offer an Immutable Mode, a transactionally updated system with a read-only root filesystem. This is essentially what our users know from Leap Micro, just integrated directly into Leap.”
For those who don’t know, Leap Micro is a specialized, lightweight, immutable, and fixed-release operating system designed for containerized workloads, edge computing, and virtualized environments. Leap Micro is not a desktop OS, but Leap is. And with Leap benefiting from what Micro already has, this could be a huge step forward.
What is immutable mode?
First off, the same blog mentions that Leap Immutable “is the way forward for container and virtual machine hosts, edge devices and anyone who prefers atomic updates with easy rollback.” It’s the last bit that should raise eyebrows, as the developers intend Leap Immutable not only for specialized deployments but for anyone who prefers atomic updates on the desktop.
Also:What is openSUSE and who is it for?
But atomic updates and immutability aren’t exactly the same thing. Does that mean Leap Immutable will be a sort of “immutable light”?
The answer is a resounding “no.” After a bit of digging, it became clear that Leap Immutable will be a fully immutable distribution.
What does that mean?
Also: Fedora Kinoite vs. Silverblue: My verdict after testing both immutable Linux distros
First off, immutable mode is a feature you can toggle during the installation, which means you can choose which version of openSUSE Leap to use: standard or immutable.
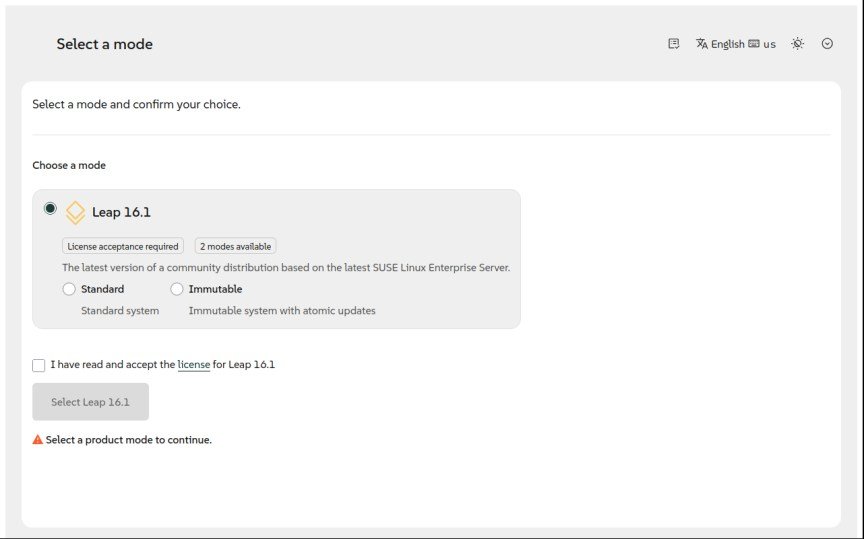
Jack Wallen/ZDNET
If you go with immutable, what that means is the root file system is mounted as read-only. I’ve previously discussed immutability in “Immutable Linux delivers serious security — here are your 5 best options.” Give that a read to find out more.
Essentially, when an OS is immutable, those directories (such as /usr and /etc) are mounted as read-only and cannot be altered. If you were to accidentally run a malicious script on an immutable system, it would be unable to alter anything in those immutable directories. That’s a serious security improvement and is also the future of Linux.
Also:5 reasons to switch to an immutable Linux distro today — and which to try first
But openSUSE Leap doesn’t just benefit from the added security of immutability, as it already includes plenty of security-focused features.
The other security layers
openSUSE was already a highly secure Linux distribution, thanks to several layers of security. Those layers are as follows.
SELinux
Up until version 15.6, openSUSE used AppArmor as its mandatory access control (MAC) security feature to restrict what system re
Also: I’ve spent years with immutable Linux – RakuOS fixed my biggest annoyance
Starting with version 16.0, openSUSE made the switch to SELinux (Security-Enhanced Linux), which was created by the NSA (in collaboration with open- to further secure Linux systems. SELinux is an incredibly powerful tool that labels every file, process, and port on a system, follows the rule of least privilege to block actions that are not allowed by specific rules, and even requires the root user to follow those rules
Firewall configuration
openSUSE makes use of firewalld as its dynamic firewall management system, which includes zones (predefined trust levels), runtime vs. permanent changes (changes that are applied but are removed upon reboot vs. changes that are permanent), and management tools (both the command-line tool, firewall-cmd, and the GUI app, firewall-config).
Also:5 Linux distros I recommend to help businesses cut costs and boost security
openSUSE’s implementation of firewalld is similar to that of most Fedora-based distributions, so it’s well known for being one of the stronger firewall implementations.
Binary hardening
openSUSE also includes binary hardening, which is the collection of default security flags and compiler options that are used during software compilation to make executable files and libraries more resilient to exploits such as buffer overflows and memory corruption.
The key hardening measures include:
- Position-independent executables (allow binaries to use random memory addresses to make it harder for hackers to predict target locations when using memory-based exploits).
- FORTIFY_SOURCE (keeps track of functions that deal with memory strings to prevent buffer overflows).
- Stack protector (injects canary values into the stack to detect and halt stack overflow attempts).
- Relocation read-only (marks the Global Offset Table as read-only to prevent function-pointer overwriting in stacks).
- Non-executable stack and heap (prevents code execution from specific data regions such as the stack or the heap to prevent arbitrary shellcode injection attacks).
Permission profiles
Permission profiles are predefined templates, specifically created to enhance security, that target file permissions, ownership, and special execution bits. The purpose of these profiles is to centralize control of permissions, enforce security during package installation and updates, and govern file modes, owners, groups, capabilities, and access control lists (ACLs) for particularly sensitive directories.
Snapper and Btrfs snapshots
Btrfs snapshots are “moment-in-time” save points of a file system subvolume, and Snapper is the SUSE tool used to automatically manage those snapshots.
Also: One of the most user-friendly Linux distros I’ve ever used is also one of the most secure
With snapshots, it is possible to easily roll back a system to a working point, so if something were to go wrong with a system, it could be restored from a previously working snapshot. With Snapper, it’s possible to configure when snapshots are taken and how many snapshots are retained.
If your system is hacked, you could effectively roll it back to a point in time prior to the hack and then take action to prevent the hack from happening again.
Regular source
Regulartandard repository. On top of that, openSUSE is built directly from theade stability and security
Put it all together
When you combine immutability with the standard openSUSE security features, it’s pretty easy to conclude that the distribution will be highly secure. Immutable distributions are already touted as some of the most secure operating systems on the market, and with openSUSE adding an immutable mode to Leap, you can be sure that it will leap ahead of the pack with regard to security.
Also:Atomic vs. immutable Linux: Why choose one when these nine distros offer both?
You can download an ISO of Leap 16.1, which includes immutable mode, from the official openSUSE download server.
